Templass.net Templass.net is self-hosted DDoS detection and mitigation software. You run it on your own network and hardware.
It detects attacks from NetFlow, IPFIX and sFlow, then mitigates with BGP blackhole (RTBH), FlowSpec, and on-demand XDP scrubbing. The operator dashboard is for the NOC. The customer panel is for each hosting customer and their prefixes. One-time license .
Demo on request.
Flow detection
NetFlow, IPFIX and sFlow. Per-group pps, bps and flow-rate thresholds, global or per vector.
BGP RTBH and FlowSpec
Blackhole and FlowSpec through embedded GoBGP. Prefix enclosure, never-blackhole whitelist, max announcements, dry run.
XDP scrubbing
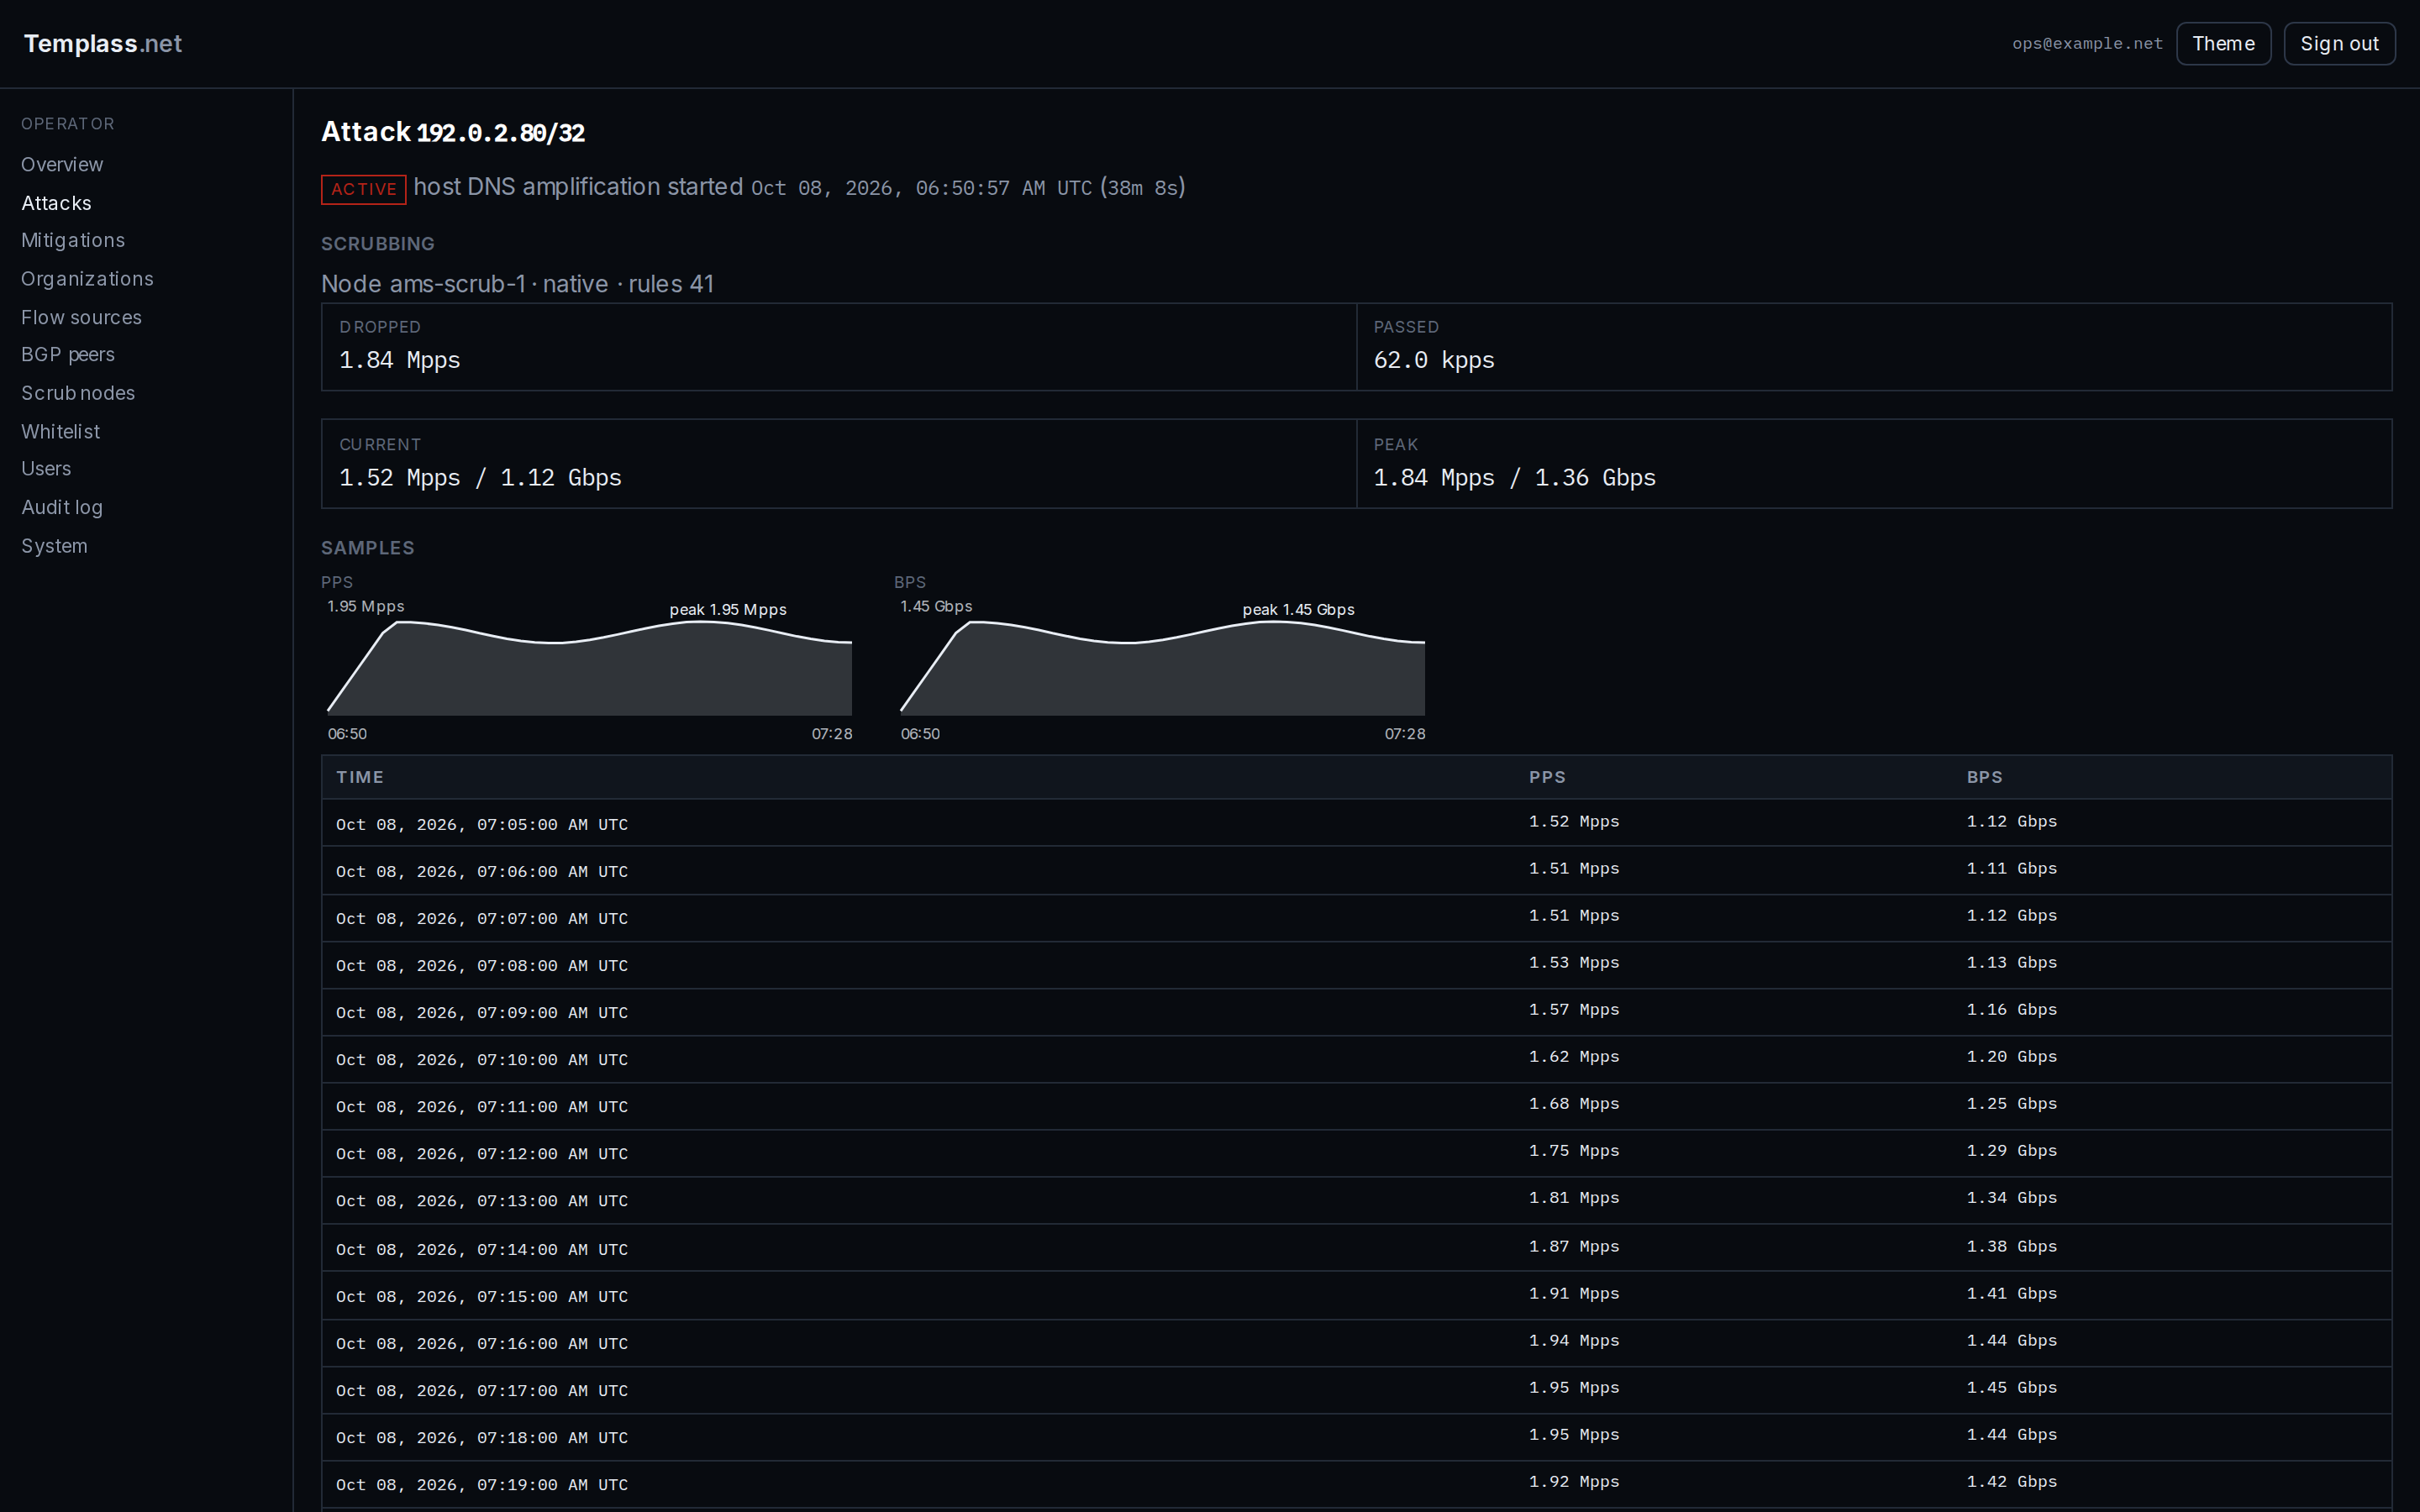
On-demand diversion of the attacked /32 or /128. Vector rules. Clean return over VLAN or GRE.
Operator and customer
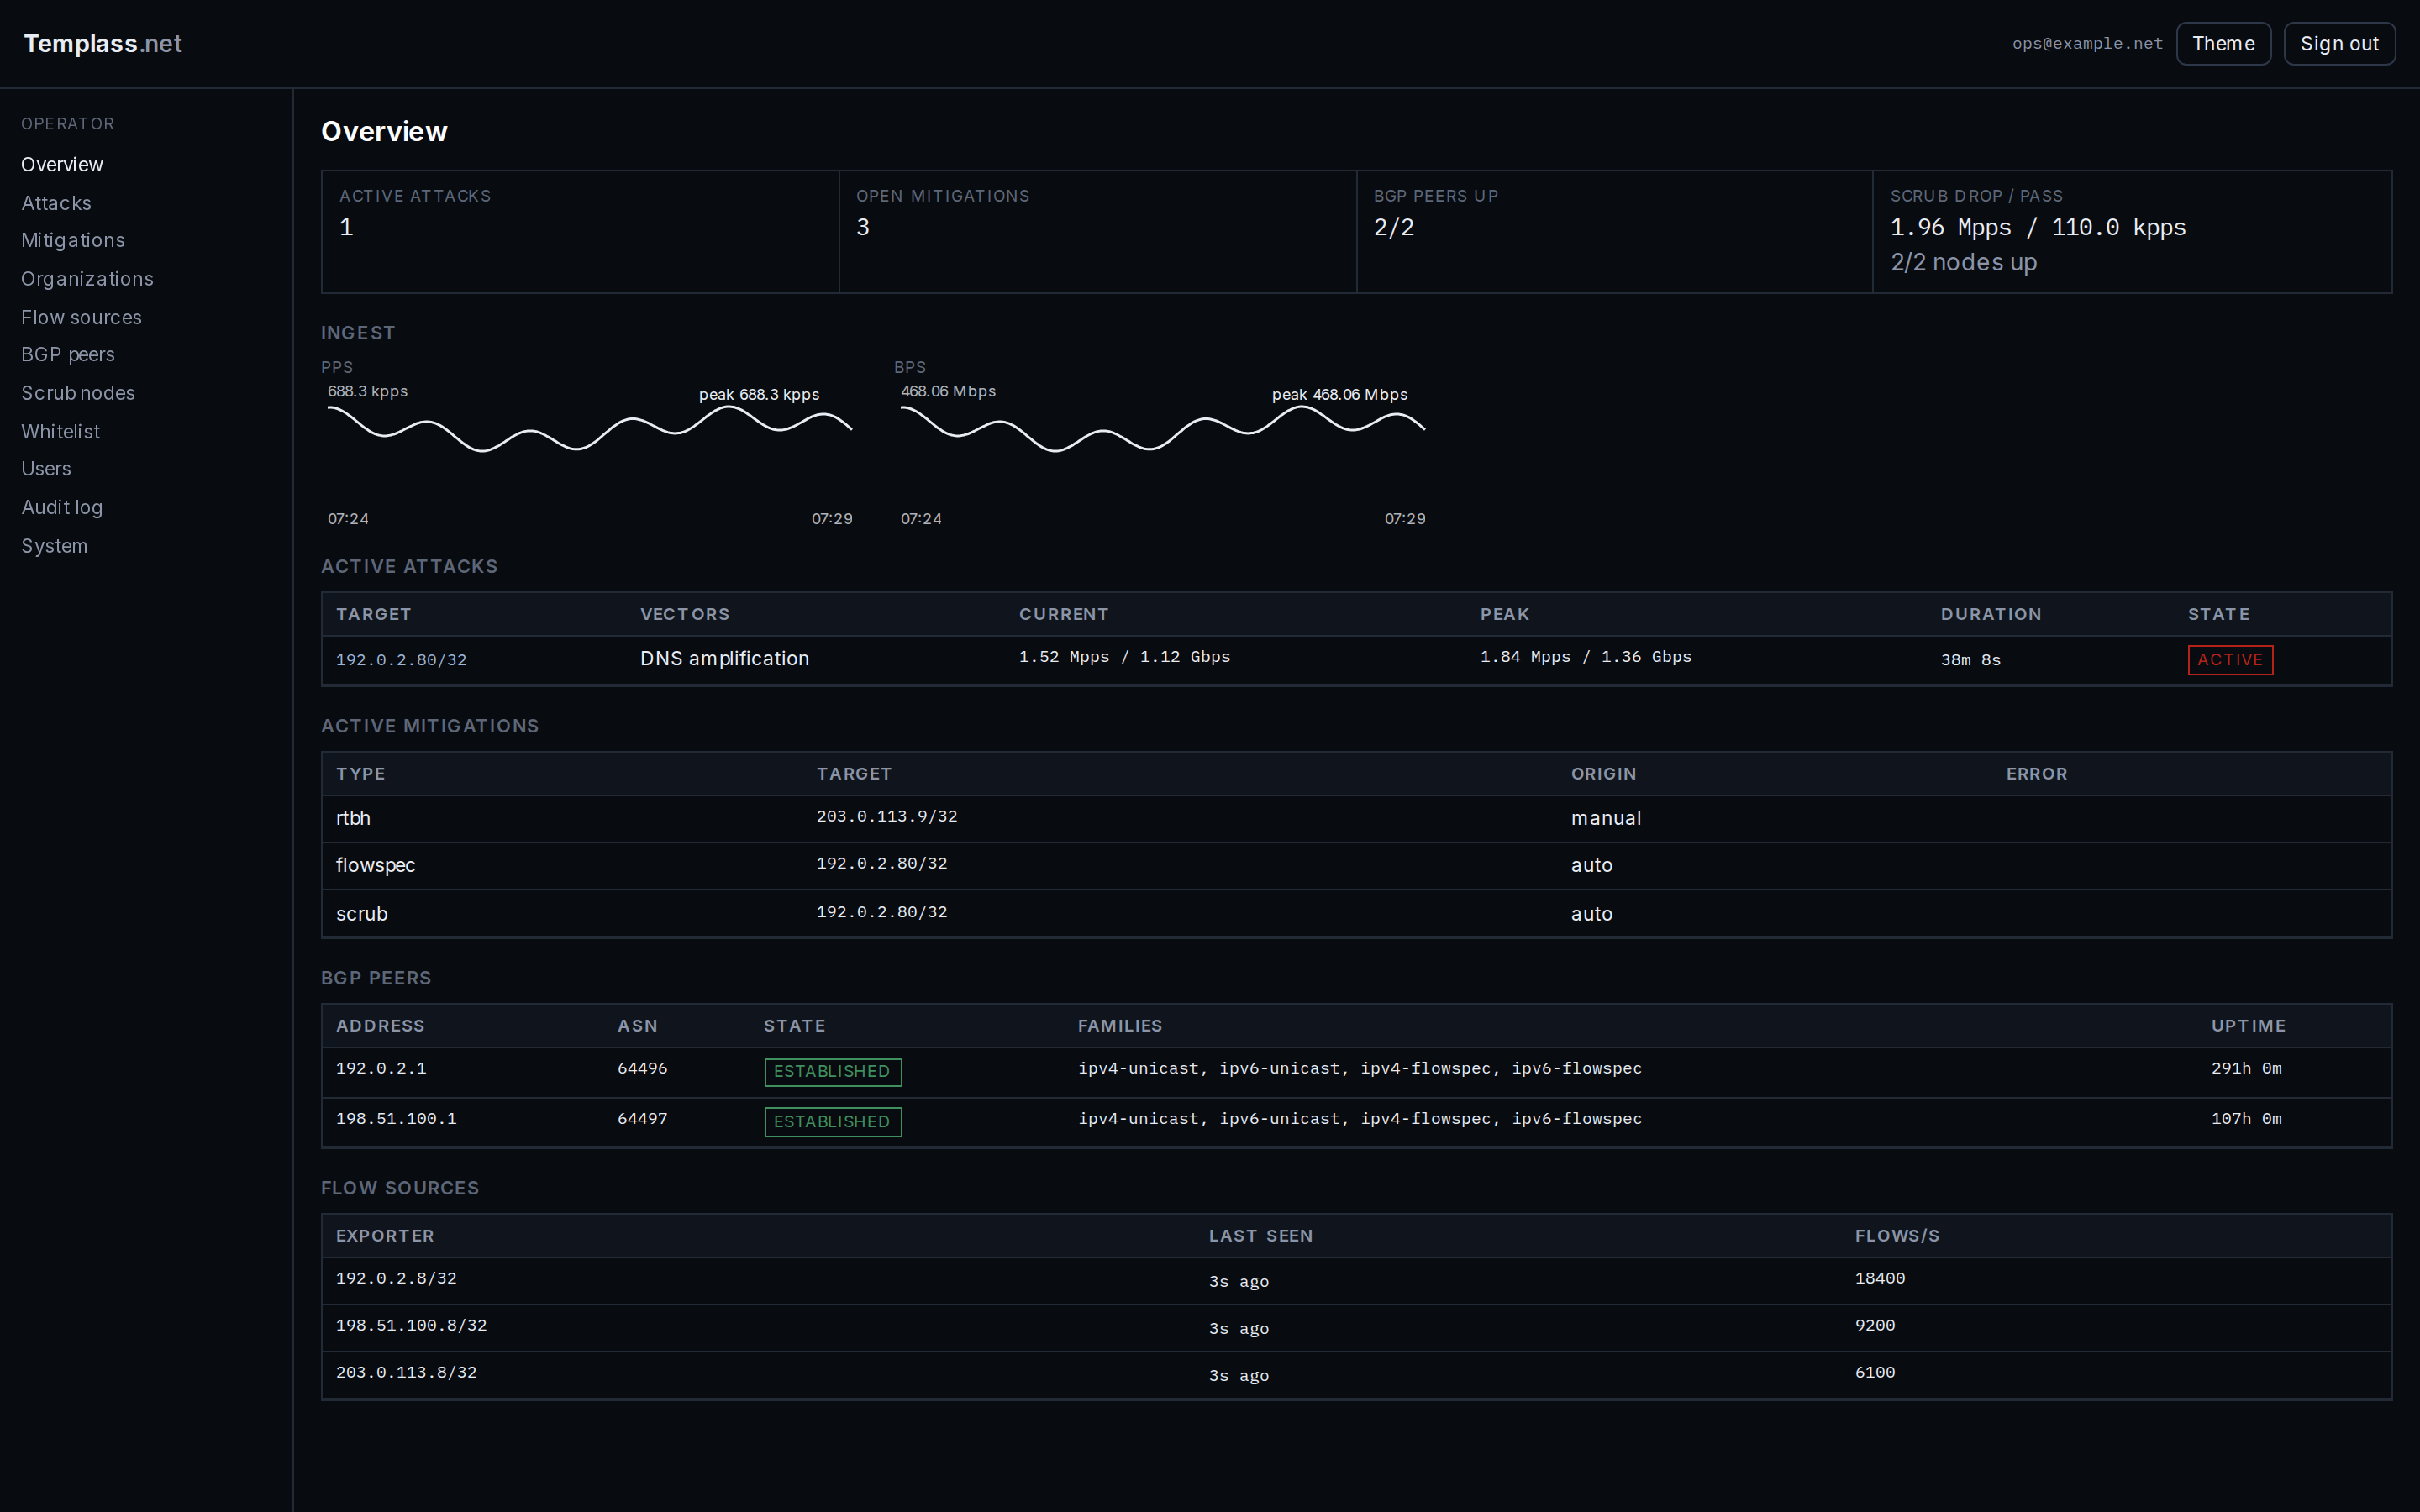
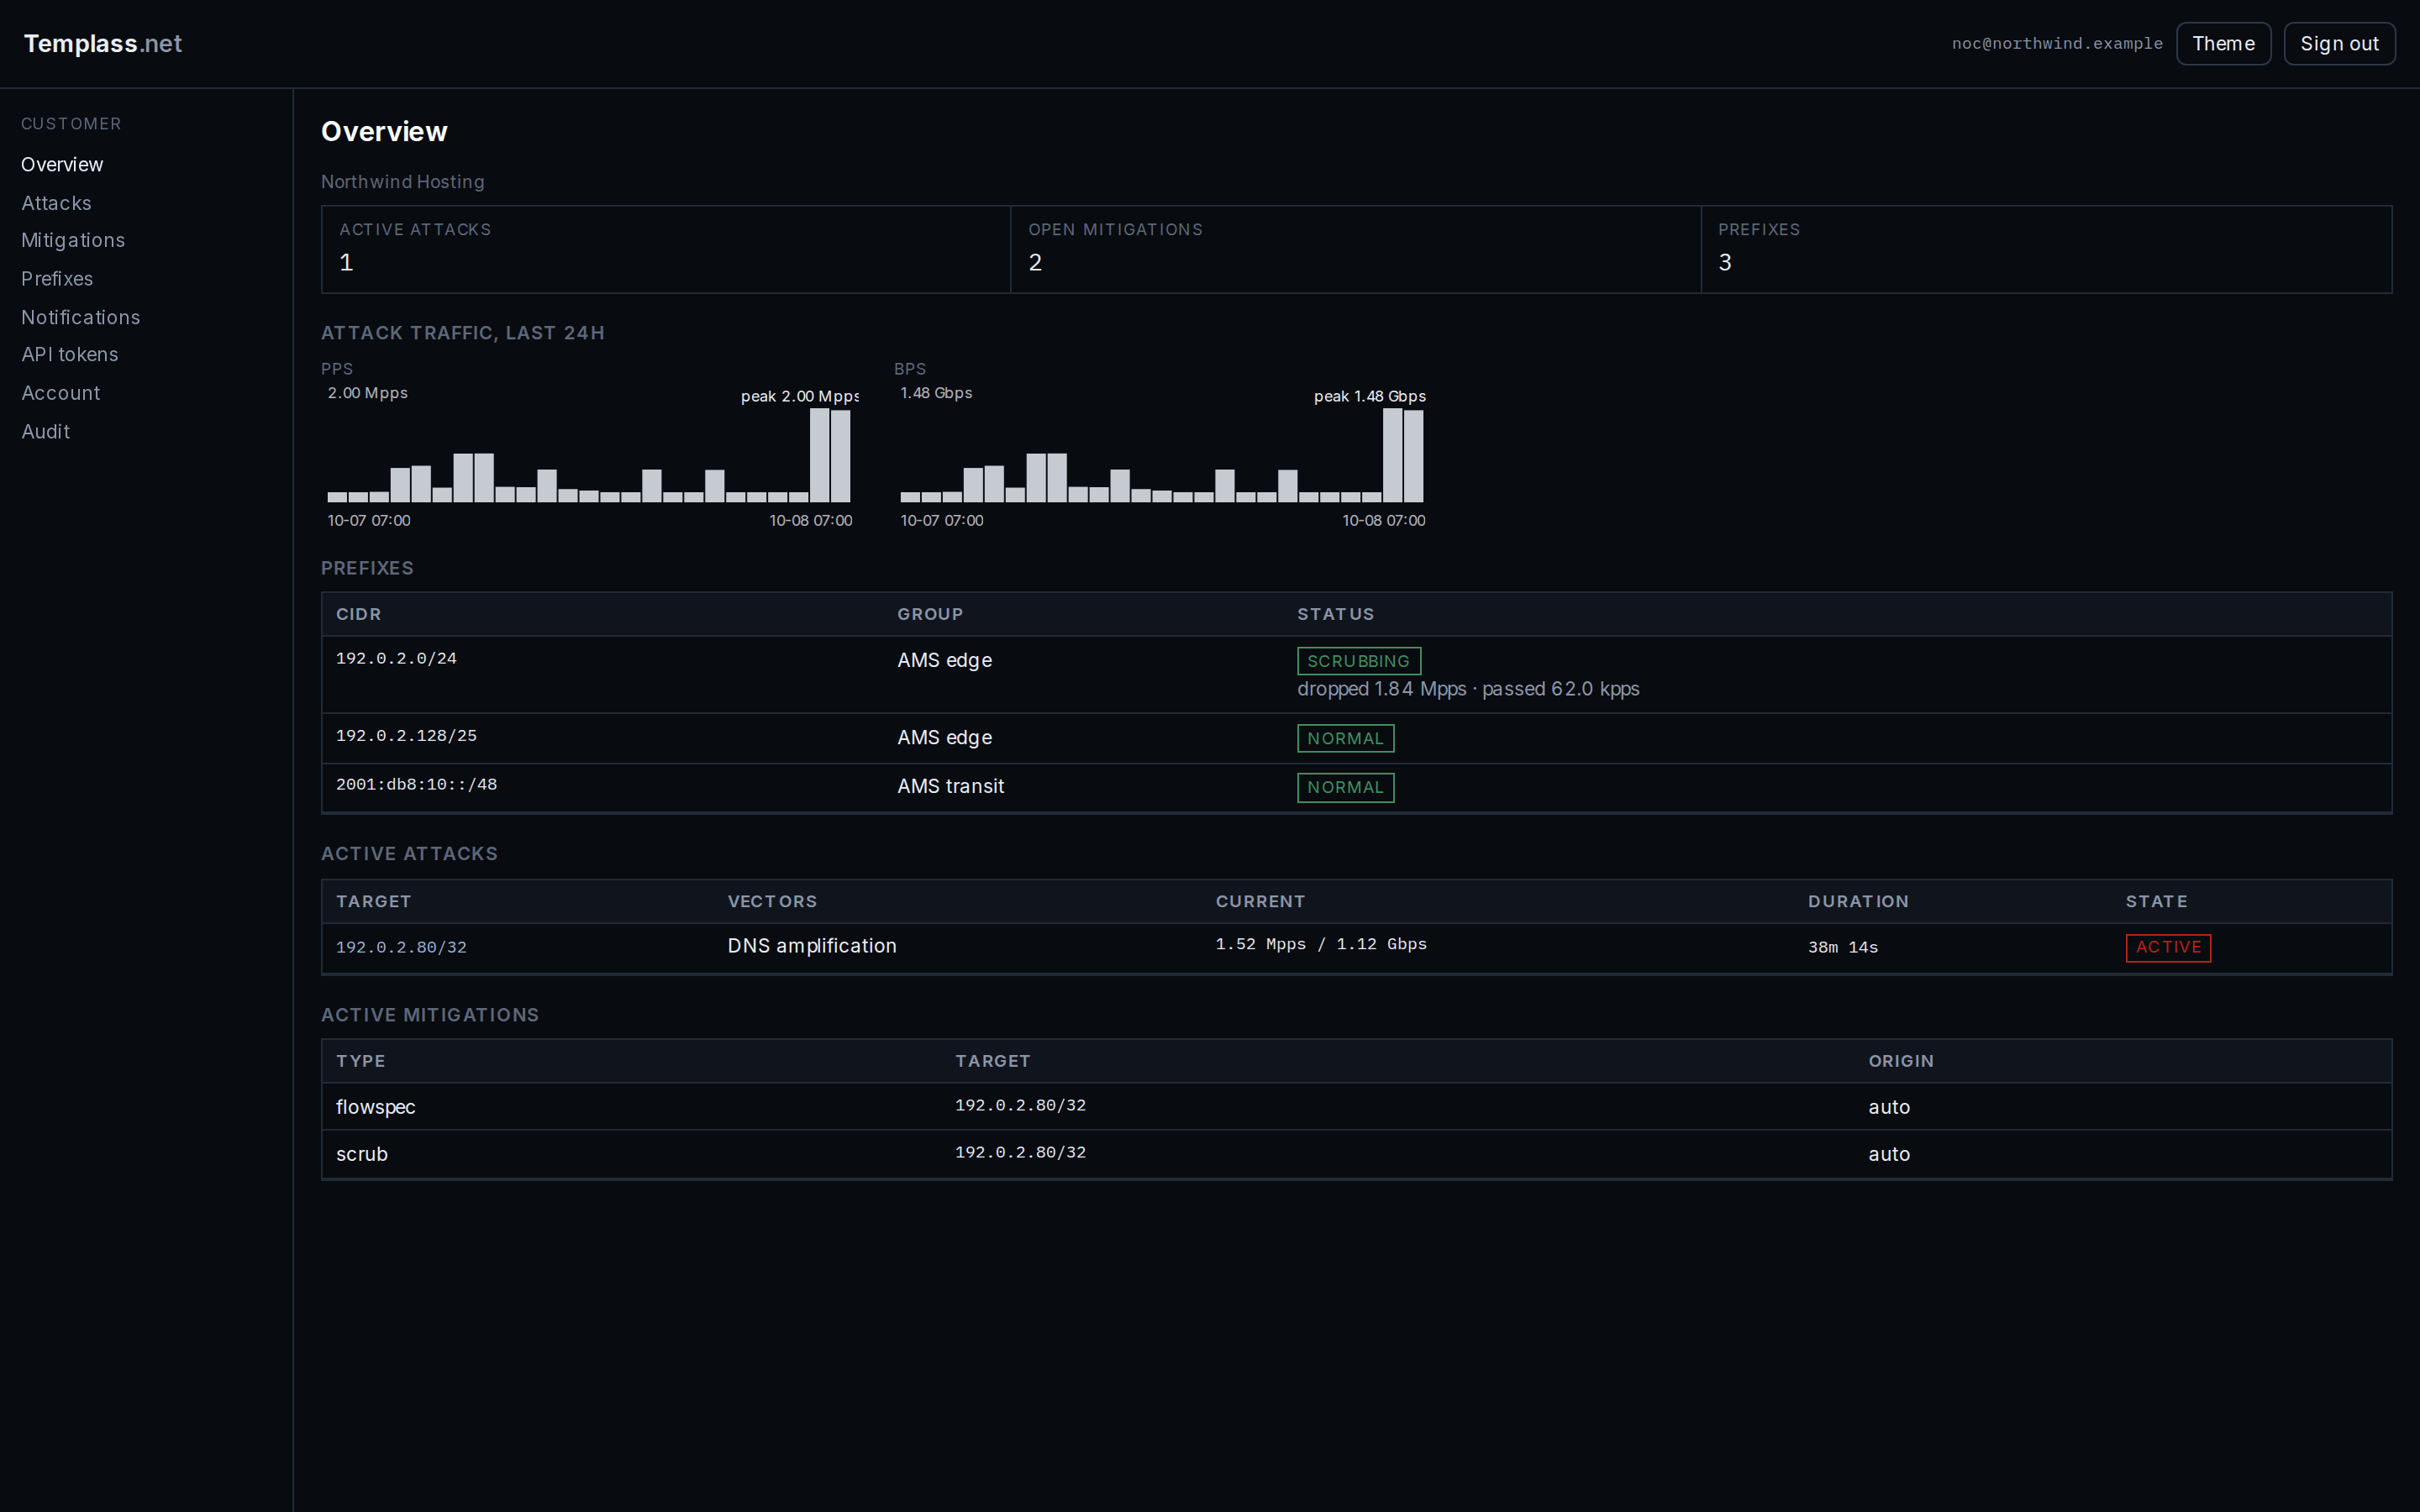
Operator dashboard for the NOC. Customer panel for each hosting customer and their prefixes.
Install
sudo ./install.sh --yes \
  --operator-email [email protected] \
  --operator-password-file /root/op.pass
Operator overview, an attack under scrub, and the customer panel. All screenshots .
Operator overview during an attack Attack detail with scrubbing Customer panel overview Hosting, VPS, game hosts
Per-customer groups, RTBH and FlowSpec, XDP scrub, customer panel.
Regional ISPs and WISPs
Prefix groups, customer-scoped mitigations, BGP you already run.
Carriers and IX-adjacent networks
Detection and mitigation inside your AS, your data, your peers.
How it works
Flows, policy, BGP, scrub diversion.
Features
Dashboard, customer panel, API, packaging.
Screenshots
Operator and customer UI.
Requirements
OS, ports, NICs, BGP peers.
Pricing
License and yearly updates.
Docs
Install, config, upgrade, license, scrub, API.